As Tanzania goes digital, who protects your privacy?
DAR ES SALAAM: AS Tanzania begins implementing its Dira 2050, which aims to build a country that uses technology to improve public services and drive economic growth towards the ambitious goal of a one-trillion-dollar economy, personal information is becoming an increasingly important part of everyday life.
This raises a fundamental question: who is protecting the personal information and dignity of Tanzanians in the digital age? For citizens today, personal information has become part of almost every service they access. When applying for a national identity (NIDA) card, personal details are collected.
When visiting a hospital, a patient’s medical history may be stored digitally. When using a bank or mobile financial services, transaction records leave a digital trail. Technology has made services easier, faster and more accessible.
But behind that convenience lies a question that is becoming increasingly important as Tanzania moves further into the digital age: are citizens’ personal details being collected, stored and used in ways that protect their right to privacy?
The question is becoming even more important as Tanzania begins implementing the National Development Vision 2050 (Dira 2050), which seeks to build a prosperous, just and self-reliant nation.
The Vision places dignity, rights and freedom among its fundamental principles, emphasising that every person deserves respect and protection of their privacy.
At the same time, Dira 2050 recognises digital technology as an important driver of development and envisages Tanzania having robust systems for managing data and information, alongside eGovernment services that are efficient and inclusive.
As the country moves towards becoming a digital nation, therefore, the question is not simply whether technology will make citizens’ lives easier, but whether these systems will protect the dignity and privacy of the people who use them.
Article 12 of the Universal Declaration of Human Rights states that no one should be subjected to arbitrary or unlawful interference with their privacy.
Similarly, Article 17(1) of the International Covenant on Civil and Political Rights (ICCPR), 1966, states that no one should be subjected to arbitrary or unlawful interference with their privacy, family, home or correspondence, nor to unlawful attacks on their honour and reputation.
Article 17(2) goes further, stating that everyone has the right to legal protection against such interference or attacks.
Tanzania already has a legal framework for protecting personal information through the Personal Data Protection Act No. 11 of 2022. The right to privacy is guaranteed under Article 16 of the Constitution of the United Republic of Tanzania as one of the fundamental human rights.
To give effect to this constitutional right, Parliament enacted the Personal Data Protection Act in November 2022.
The law received presidential assent in December 2022 and came into force on May 1, 2023. The Act establishes a legal framework governing the collection, processing, use, storage, disclosure and transfer of personal data.
It also protects the rights of data subjects and sets out obligations for those who collect and process personal information.
Under Section 6 of the Act, the Personal Data Protection Commission (PDPC) was established on May 1, 2023, as an independent regulatory authority responsible for overseeing and ensuring compliance with the law.
The Commission was officially launched by President Dr Samia Suluhu Hassan on April 3, 2024, marking a significant step towards the full implementation of its mandate.
Among the Commission’s responsibilities are registering data controllers and processors, educating the public about personal data protection, monitoring compliance with the law, investigating complaints and breaches involving personal data, issuing regulatory guidance, and advising the government on matters relating to personal data protection and privacy.
For citizens, the framework provides a range of rights over their personal information.
These include the right to be informed about how their information is being used, to access their data, to request corrections, to request deletion in circumstances permitted by law, to restrict processing, to object to certain uses, to withdraw consent, and to lodge complaints.
However, having a law and a regulatory institution is one thing; enforcing those protections in practice is another.
ALSO READ: The price of virality: Privacy in Tanzania entertainment
According to Commission figures, by May 2026, more than 14,400 organisations had been registered, more than 340 complaints had been received and four decisions had been issued.
In addition, more than 39 permits for the transfer of personal data outside the country had been granted. These figures suggest that Tanzania’s personal data protection system is continuing to take shape.
They also raise questions about how effectively the system works in practice and the extent to which ordinary citizens are able to exercise the rights provided to them by law.
The Personal Data Protection Act, 2022, sets out requirements governing how personal information should be collected, processed and used.
In everyday life, challenges may arise when personal information is used without a lawful basis or disclosed to third parties without following the required procedures.
Such challenges can arise across a range of services, including financial institutions, telecommunications companies and healthcare providers that collect customers’ personal information.
One of the challenges facing citizens is unsolicited marketing messages, commonly known as spam, in which individuals or organisations send promotional messages without the recipient requesting such services.
Speaking recently to journalists in Dodoma, the Director General of the PDPC, Dr Emmanuel Mkilia, said the Commission had begun compliance inspections under the Personal Data Protection Act, Chapter 44, visiting institutions, organisations and businesses that collect and process personal data across the country.
He said the inspections were intended to establish whether data controllers and processors were complying with the requirements of the law in their operations.
“Among the issues to be inspected are the registration of institutions in the Commission’s register, the implementation of the duties of the Data Protection Officer (DPO) in the respective institutions, and how personal data are collected, processed and stored to ensure that the procedures established by law are followed,” said Dr Mkilia.
This demonstrates that personal data protection is not simply about protecting information from hacking. It also concerns what happens to information after it has been collected.
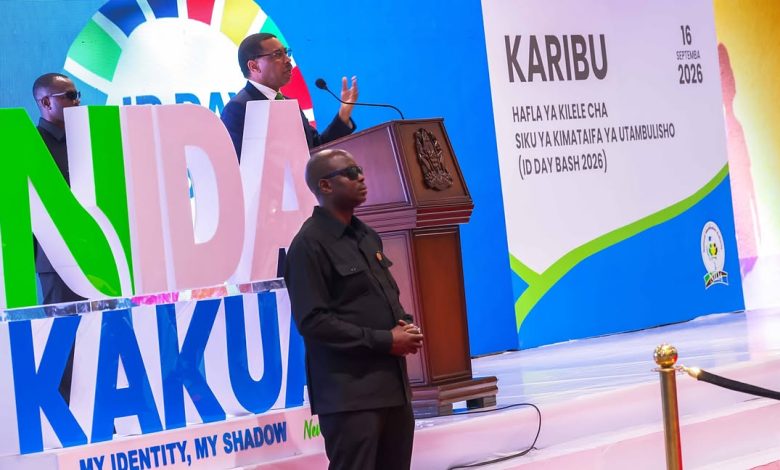
The National Identification System is a good example of the importance of personal information in modern service delivery. NIDA systems operate within the framework of the Personal Data Protection Act No. 11 of 2022.
Under the law, NIDA has a legal obligation to ensure that personal data are not used for purposes other than those for which they were collected, including identification and registration, without the consent of the individual. Oversight in this area is also carried out in coordination with the PDPC.
When citizens seek NIDA services, they provide information that can personally identify them.
NIDA also operates online services involving the use of the National Identification Number (NIN) and other identification details. According to figures from the Ministry of Home Affairs, between July 2025 and April 2026, NIDA registered and identified 1,145,334 people aged 18 and above, compared with 844,994 people registered and identified during the same period in 2024/25.
This brought the total number of people registered and identified to 27,186,421.
During the same period, NIDA issued NINs to 857,244 people, bringing the total number of people who had received identification numbers to 22,654,206.
NIDA also connected 17 institutions to its Registration and Identification System, bringing the total number of connected institutions to 147, comprising 66 public institutions and 81 private institutions.
However, according to report issued by the Minister for Home Affair Patrobas Katambi on September 16, this year a total of 2,027,103 national identity cards remain at NIDA’s offices out of 21,526,635 cards produced.
By September 16 this year, the authority has registered 27,520,835 people and issued 23,515,667 NINs. According to the Ministry, the move is part of government efforts to ensure that systems operated by institutions providing services to citizens can communicate with one another, making access to services easier.
But as more institutions become connected to the national identification system, it becomes increasingly important to ensure that citizens’ information is used only for its intended purposes and receives appropriate protection.
As these systems become more interconnected, an important question remains: who can access citizens’ information, for what purposes and under what conditions? Alongside the expansion of technology, Tanzania is also facing the growing challenge of cybercrime.
According to the Ministry of Home Affairs, reported cybercrime offences recorded at police stations increased from 748 in 2024/25 to 1,323 between July 2025 and April 2026.
The ministry said the increase was also attributed to the use of modern investigative tools, operations, online patrols and a positive response from citizens in reporting cybercrime.
For the 2026/27 financial year, the ministry, through the Tanzania Police Force, said it would continue efforts to combat cybercrime, including the misuse of social media and the hacking of online information.
Among the measures announced were the establishment of zonal cybercrime investigation offices in Dodoma and Zanzibar, the introduction of systems to monitor cyberattacks, and the strengthening of a specialised unit responsible for addressing misinformation and incitement online.
These measures demonstrate that information security is an important part of building a digital nation.
However, information security cannot be separated from the question of privacy because, as digital systems expand, so does the amount of information being collected and stored.
NIDA is not the only area where large amounts of personal information are processed. In the health sector, digital systems can store patients’ medical records, treatment histories, test results and other sensitive information.
Technology can make information easier to access and improve service delivery, but it also creates a responsibility to ensure that such information remains secure.
In recent years, mobile financial services have transformed the way Tanzanians conduct transactions. Dira 2050 itself identifies the growth of digital financial services as part of the transformation that can increase financial inclusion.
These services have made financial transactions more convenient and expanded access to financial services. But every digital transaction also generates information about the user.
Account details, transaction records and patterns of financial service use are all forms of information that require protection.
Overall, digital systems such as NIDA, health information systems and banking services can improve access to services, make citizens’ lives easier and increase the efficiency of service delivery.
However, these benefits can also come with challenges, including data breaches, the digital divide, limited awareness among some citizens about technology and their rights, inadequate access to modern digital tools and cybercrime. If not properly addressed, these challenges can threaten citizens’ privacy and dignity.
In the telecommunications sector, the Tanzania Communications Regulatory Authority (TCRA) has an important role in regulating communications services and matters relating to users’ information.
This environment covers the registration of SIM cards, the storage of information, the security of communications, and the use of such information in accordance with the law.
Under the Electronic and Postal Communications (SIM Card Registration) Regulations, 2020, the misuse of customers’ personal data or information collected during SIM registration, including fingerprints or NIDA numbers, is prohibited.
The regulations also establish a specific offence relating to the misuse of customer information. Regulation 20 provides that a licensee, dealer or agent who misuses customer information collected for SIM registration commits an offence.
A person found guilty may face a fine of not less than five million Tanzanian shillings, imprisonment for not less than 12 months, or both.
However, statistics published in the quarterly Communications Sector Performance Report for the quarter ending June 2026 show that reported fraud attempts fell by 25.29 per cent, from 9,816 attempts in the quarter ending March 2026 to 7,334 in the quarter ending June 2026.
The decline is an indicator of the measures being taken to combat fraud and cybercrime threats. However, a reduction in reported fraud attempts alone is not enough to measure the overall level of protection of citizens’ privacy and personal information.
According to communications specialist and Executive Director of Amtec Consulting Limited, Engineer Jameson Kasati, Tanzania still has gaps in cybersecurity.
He said that despite ongoing efforts, banks, telecommunications companies and the police still do not share information about fraud quickly enough. He said delays in sharing such information give criminals an opportunity to continue carrying out attacks before action can be taken.
The expert also said the National Cybersecurity Strategy 2022–2027 and the Cybersecurity Centre require more resources and greater powers to perform their roles effectively.
“We need a single platform where phone companies, banks, and police can instantly share fraud alerts. If a fraud pattern is spotted in one place, everyone should know about it within minutes. This will help stop attacks from spreading,” said Eng Kasati.
He added that stronger enforcement of SIM registration had contributed to a decline in fraud attempts, but that further measures were needed.
Among his recommendations were the use of biometric verification, such as fingerprints or facial recognition, when registering or swapping SIM cards, as well as stronger action against telecommunications employees who assist criminals.
Meanwhile, the National Coordinator of the Tanzania Human Rights Defenders Coalition (THRDC), Onesmo Olengurumwa, in an advisory statement on the state of privacy and communications security in Tanzania, urged citizens and society at large to stop sharing other people’s personal information, saying that doing so is contrary to the law.
Mr Olengurumwa said TCRA, through its Consumer Protection Committee, should ensure that it fulfils its responsibility to protect customers’ information and ensure that service providers who violate customers’ right to privacy are held accountable and appropriate action is taken against them.