25 YEARS AFTER 9/11: Why cyber resilience matters more than ever
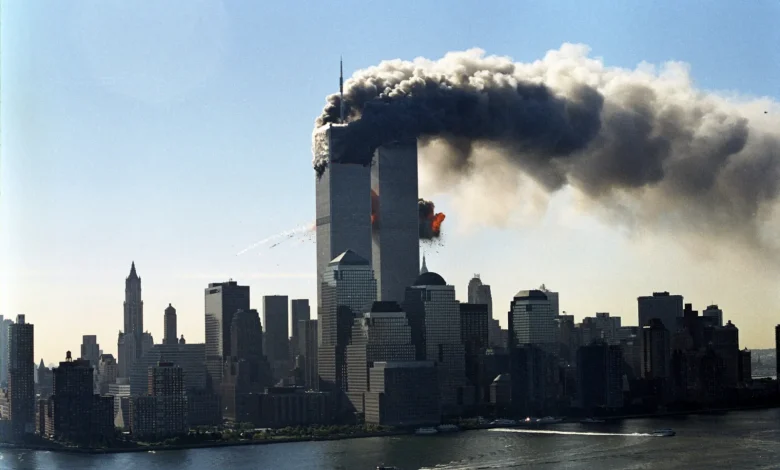
TWENTY-five years ago, on September 11, 2001, the world witnessed an event that fundamentally changed the way governments, businesses and ordinary people thought about security.
The terrorist attacks in the United States caused enormous loss of life and disruption. Beyond the immediate tragedy, September 11 exposed an important reality: major disruption can arrive suddenly, affect interconnected systems and force organisations to operate under conditions they had never imagined.
Today, the nature of some of the threats facing society has changed. Increasingly, disruption can begin not with a physical attack, but with a few lines of malicious computer code, stolen passwords, compromised suppliers or an attack on critical digital infrastructure.
The lesson from September 11 therefore remains relevant: security is important, but resilience is equally important.
From preventing attacks to surviving disruption
Before major crises occur, organisations naturally concentrate on prevention. They install security systems, develop procedures and try to stop bad things from happening.
But no security system can guarantee that every incident will be prevented.
This is where resilience becomes important.
Cyber resilience is the ability of an organisation to prepare for cyber incidents, withstand them, continue delivering essential services, recover quickly and learn from what happened.
Cybersecurity asks: How do we protect ourselves from attack?
Cyber resilience adds another question: If an attack succeeds, can we continue operating?
That difference is becoming increasingly important. Our dependence on digital systems has grown.
In 2001, the world was already becoming digital, but our dependence on technology was far smaller than it is today.
Twenty-five years later, banking, telecommunications, aviation, hospitals, government services, electricity, transport, education and businesses increasingly depend on digital networks.
In Tanzania, millions of people now use mobile phones and digital financial services as part of everyday life. Businesses depend on internet connectivity, cloud services, electronic payments and digital communication. Government institutions are also expanding online services.
This digital transformation brings enormous benefits. But it also creates new forms of vulnerability.
Imagine a major bank being unable to process transactions for several hours. Imagine mobile money services becoming unavailable, a hospital losing access to important systems, or a government digital platform becoming inaccessible.
The physical buildings might still be standing, employees may be ready to work, but essential services could nevertheless be severely disrupted.
That is why cyber resilience should no longer be regarded simply as an ICT issue.
It is a business continuity and national resilience issue.
Expect the unexpected
One of the enduring lessons from September 11 is the danger of planning only for events we consider likely.
Modern organisations need to cussed ask difficult questions.
What happens if our main data centre becomes unavailable? What happens if ransomware locks important systems?
What if our internet connection fails? What if a trusted supplier is compromised? What if employees cannot access their normal workplace or systems? These questions should be discussed before a crisis, not during one.
Organisations therefore need tested business continuity and disaster recovery arrangements. Important information should be securely backed up, and organisations must know how quickly critical systems can be restored.
Having a recovery plan sitting in a document is not enough. It must be tested.
Resilience requires redundancy
Another important principle is avoiding excessive dependence on a single system, supplier, communication route or location.
Engineers understand this very well. If one component fails, and other should be capable of taking over.
The same principle applies to cyber resilience.
An organisation may need alternative internet connections, backup systems, geographically separated recovery facilities and alternative communication channels.
For critical services, redundancy may appear expensive when everything is working normally. During a major disruption, however, it can become the difference between continuing operations and shutting down.
Boards and senior executives should therefore stop viewing resilience expenditure purely as a technology cost. It is closer to an insurance policy protecting the organisation’s ability to operate.
People remain at the centre
September 11 also demonstrated the importance of people, leadership and communication during emergencies.
Technology alone cannot create resilience.
Employees must know what to do when normal systems fail. Management must understand who has authority to make emergency decisions. Communication channels must be established before an incident occurs.
Cyber exercises can help.
Instead of simply telling employees that a cyber incident might happen, organisations can simulate realistic scenarios.
Suppose the finance system becomes unavailable on Monday morning. What happens next? Who is contacted? Can salaries or suppliers still be paid? How does the organisation communicate with customers? Who speaks publicly? When should regulators or law-enforcement authorities be informed?
Exercises reveal weaknesses that ordinary audits may not identify.
Cyber resilience must reach the boardroom
Perhaps the biggest change needed today is recognising that cyber resilience cannot remain the responsibility of the ICT department alone.
A major cyber incident can affect revenue, reputation, customers, regulatory obligations and even the survival of an organisation.
Boards should therefore ask management straightforward questions.
Which systems are absolutely critical to our operations? How long can we operate without them? How quickly can we recover? When did we last test our backups? What happens if our most important technology supplier fails?
The quality of the answers may tell directors more about organisational resilience than a long technical report.
A lesson for Tanzania
As Tanzania continues its digital transformation, resilience should be built into that journey from the beginning.
Banks, telecommunications companies, government institutions, hospitals, utilities and other providers of essential services need strong cybersecurity. But they also need the ability to continue operating when preventive controls fail.
Small and medium-sized businesses should think similarly. They may not require expensive disaster recovery centres, but they can maintain secure backups, alternative communication arrangements, incidentresponse contacts and simple business continuity plans.
The principle is the same regardless of organisational size: do not wait for disruption before deciding how you will respond to it.
From security to resilience
September 11, 2001 reminds us that the world can change unexpectedly and that systems we depend upon can suddenly be disrupted.
Twenty-five years later, our societies are more connected, more digital and more dependent on technology than ever before.
The threats have also evolved.
Cyberattacks can cross borders in seconds. Criminals can attack organisations thousands of kilometres away. Artificial intelligence is giving defenders powerful new capabilities, but it can also help attackers automate and improve some of their methods.
The answer cannot be fear or resistance to digital transformation.
It must be preparedness and resilience.
The strongest organisation is therefore not necessarily the one that believes it can prevent every attack. It is the one that accepts incidents may happen, prepares for them, detects them quickly, continues essential operations, recovers safely and learns from every experience.
That may be one of the most important lessons September 11 can offer today’s digital world:
We cannot predict every crisis. But we can prepare our organisations and societies to withstand disruption, recover and continue moving forward